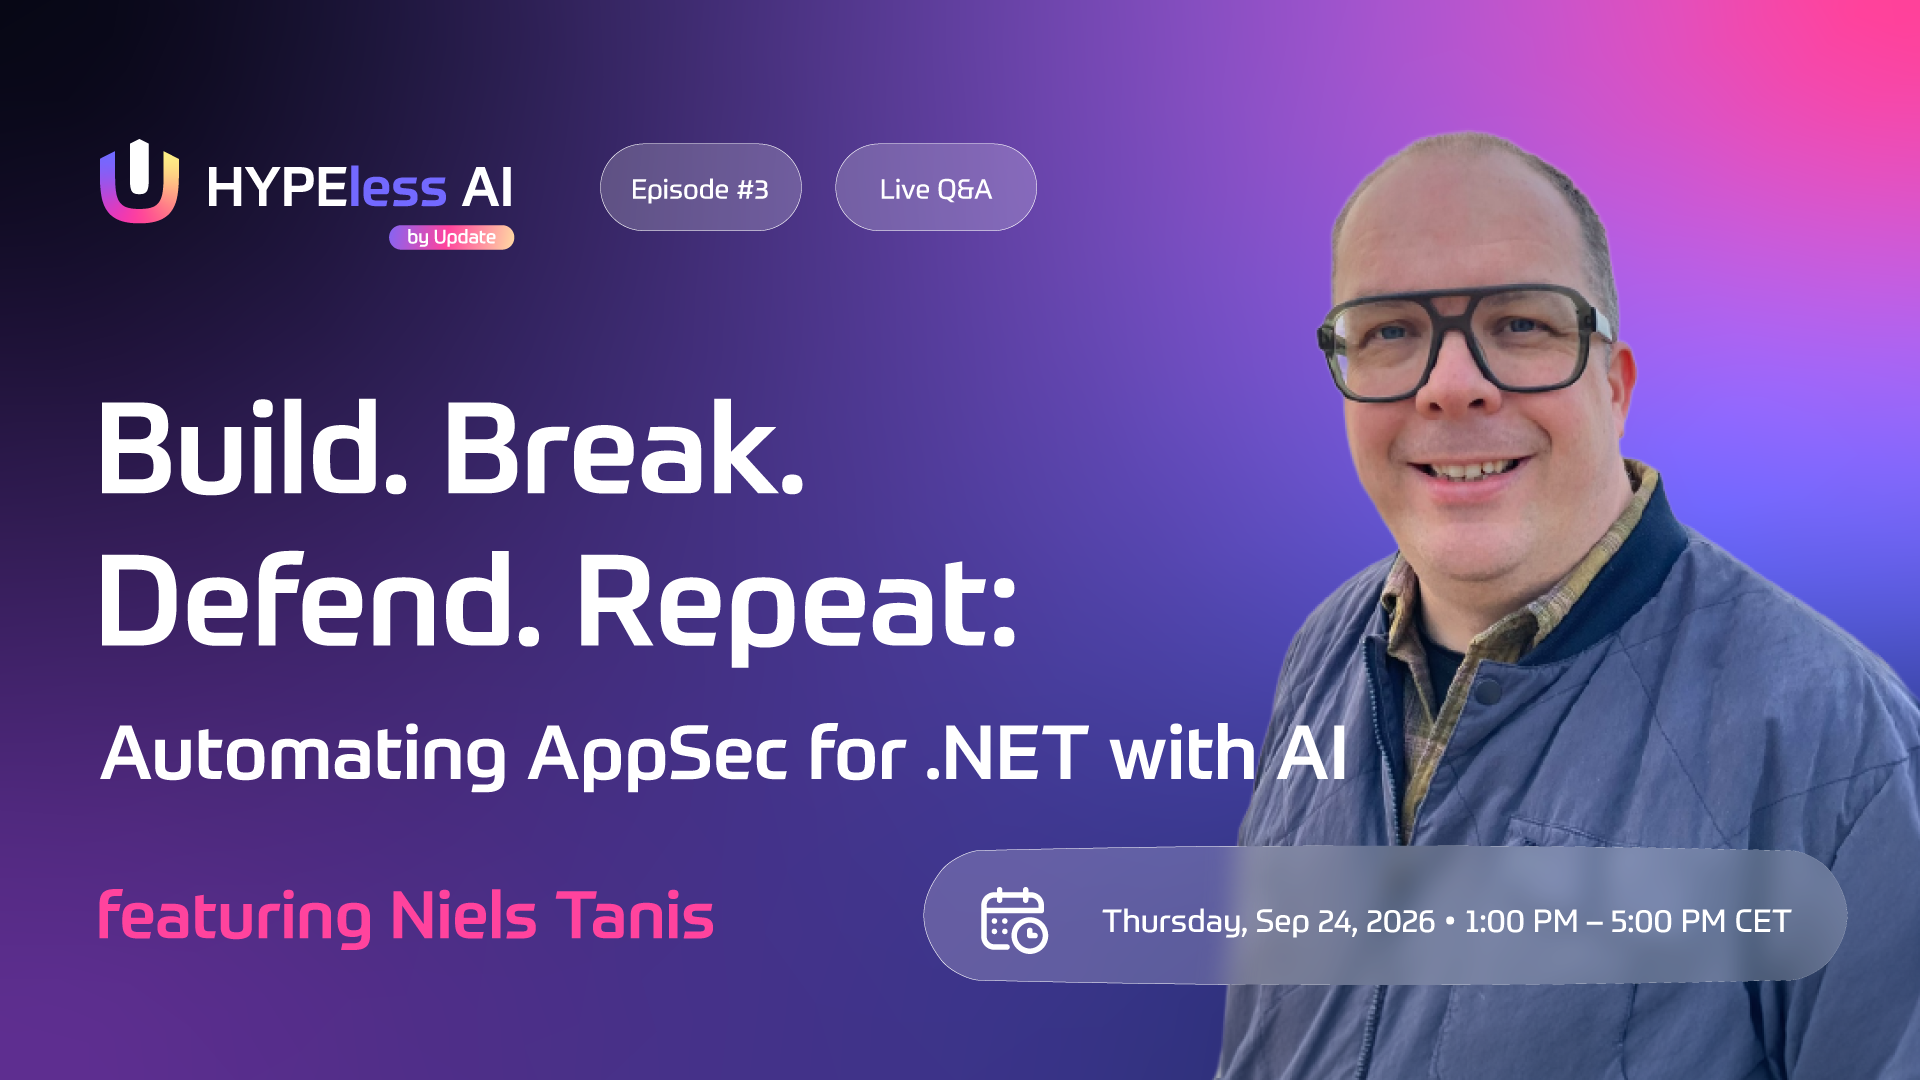
Hypeless AI #3: Build. Break. Defend. Repeat: Automating AppSec for .NET with AI

Past Episode

#3: Build. Break. Defend. Repeat: Automating AppSec for .NET with AI

Thu, Sep 24, 2026 • 1:00 PM – 4:30 PM CEST

AI is changing not only how we build software, but also how vulnerabilities are discovered and exploited. In this session, you’ll see how AI can help you find security flaws in .NET applications, test and break your own code, and fix vulnerabilities before attackers do. We’ll explore practical ways to combine AI with proven security tools and integrate AppSec into your everyday development workflow, continuously, not just at the end of the project.

The goal isn’t to overwhelm you with tools, but to show practical patterns you can start using immediately. All of this is available today, and you can start using it right away. If you’re struggling to keep up with the pace of AI and wondering how to stay relevant as a developer, this episode is for you.

Recordings

Buy Online Individual Ticket for 1 person
49€ 1189 CZK incl. VAT
Buy Online Team Ticket for up to 4 people
139€ 3369 CZK incl. VAT
Watch free
preview
Event recording 4 hours of useful content

Schedule

13:00–14:00
Build & Break | PART 1

AI writes a lot of your code now, and some of it is vulnerable. That goes for the code it generates, and for the LLM calls and agents you're wiring into your own applications. Meanwhile, frontier models have started finding vulnerabilities on their own and at scale. One recent run surfaced 23,000 of them across 1,000 open source projects, most absent from any CVE database. This first part covers the build and break sides of the loop. We start with what AI-generated code gets wrong and the new attack surface you inherit when you build LLMs into your apps. From there we dig into LLM-driven pentesting and security testing. And here's the good news: you don't need a frontier lab's budget for this. With deterministic analysis and off-the-shelf models, you can find and break vulnerabilities in your own code yourself. That's what we're going to do in part two!
Intro Demo
14:15–15:15
Defend & Repeat | PART 2

Attackers can now discover bugs faster than any human AppSec team can keep up with, so defence has to run at machine speed too. The catch: an LLM on its own hallucinates, and a rule-based scanner on its own buries you in false positives. The useful combination is deterministic analysis for the verifiable facts (call graphs, data flows, dependency trees, known CVEs) plus an LLM that understands what the code does. In this second part we put that combination to work on a real .NET application, using AI agents with composable skills: threat modelling generated from the code itself, static analysis with AI-assisted fixing, and CVE triage that checks whether vulnerable dependency code is even reachable before you spend time on it. Then comes the repeat: how to fit all of this into your own workflow so it runs on every commit, not just once. You'll see what works today and where it still breaks.

Demo
15:30–16:30
Live Q&A: Ask me anything

I'll answer all the questions you post during the show.

Q&A

Speakers

Niels Tanis
Niels Tanis

Niels Tanis has got a background in .NET development, pentesting and security consultancy. He is Microsoft MVP and has been involved in breaking, defending and building secure applications. Right now he is a software security engineer at Tidalis and before that he was a security researcher at Veracode where he focussed on static analysis of a variant of languages. He is married, father of two and lives in a small village just outside Amersfoort, The Netherlands.